Turn Terraform HCL into a CloudFormation template in JSON, with variables as Parameters, outputs as Outputs and references as intrinsic functions such as Ref and Fn::GetAtt.
This looks like it contains a secret.
Your code is sent to an AI service for conversion. Replace real keys and tokens with placeholders before converting.
How to convert Terraform to a CloudFormation template
To convert Terraform to CloudFormation, paste your HCL into the editor above and press Convert to CloudFormation. Each resource becomes a typed entry under Resources, variables become Parameters, outputs become Outputs and references become Ref, Fn::GetAtt or Fn::Sub. Then validate the JSON template, review a change set and create the stack.
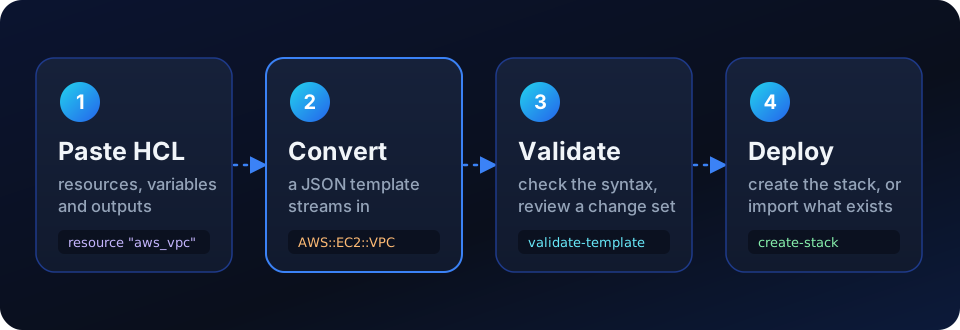
Add your TerraformPaste HCL into the Terraform (HCL) editor, use Open file for a .tf, .hcl or .txt file up to 500 KB, or drop one onto the editor. Include the variable and output blocks. Sample loads a VPC, a subnet and a security group.
Let the secret check runTerraform variables sometimes hold real keys or passwords. The page flags AWS access keys, secret keys, private keys and common API tokens before anything is sent, so you can replace them first.
Convert to CloudFormationClick Convert to CloudFormation or press Ctrl + Enter. The template streams in as it's written, and Stop cancels it. Each conversion takes up to 60,000 characters, so convert one module at a time.
Review the templateCheck the logical IDs, parameter defaults and resource list. JSON has no comments, so Terraform features with no CloudFormation equivalent are left out rather than flagged. Copy the result or Download it as template.json.
Validate and deployRun aws cloudformation validate-template, create a change set to preview the resources, then create the stack. If the resources already exist, import them instead of creating new ones.
Converting is step two. Validating and previewing the change set come before anything is created.
Why convert Terraform to CloudFormation
The usual reason is a platform standard. Organizations that roll infrastructure out with CloudFormation StackSets across accounts, or through AWS Control Tower customizations, need templates rather than HCL. Others want CloudFormation to keep track of resources so they no longer run a Terraform state backend, or they're handing infrastructure to a team that already reviews change sets.
Rewriting HCL by hand means looking up the resource type and property name for every Terraform argument. aws_security_group ingress blocks become SecurityGroupIngress entries with IpProtocol and CidrIp, tag maps become lists of Key and Value pairs, and every reference becomes an intrinsic function. The converter drafts the whole template so your time goes on the parts that need judgment.
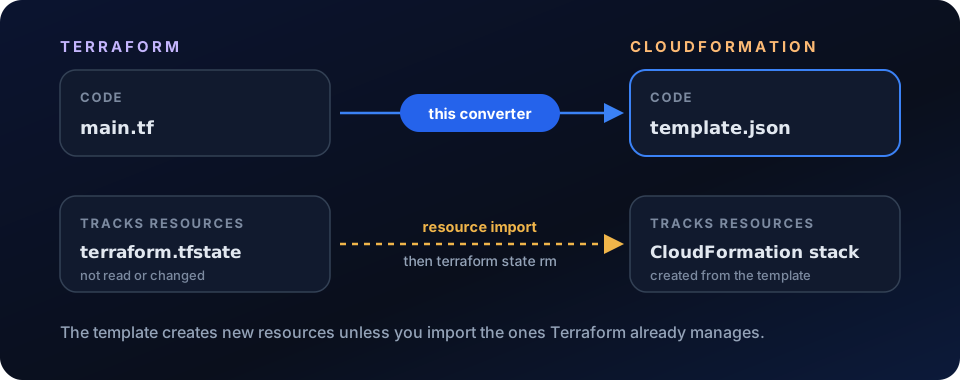
It rewrites code only. It doesn't read your state file or your AWS account, so the template describes resources to create. To bring existing resources under CloudFormation, use resource import. To go the other way, use the CloudFormation JSON to Terraform converter.
The converter moves code, not ownership. Existing resources need an import.
How Terraform concepts map to CloudFormation
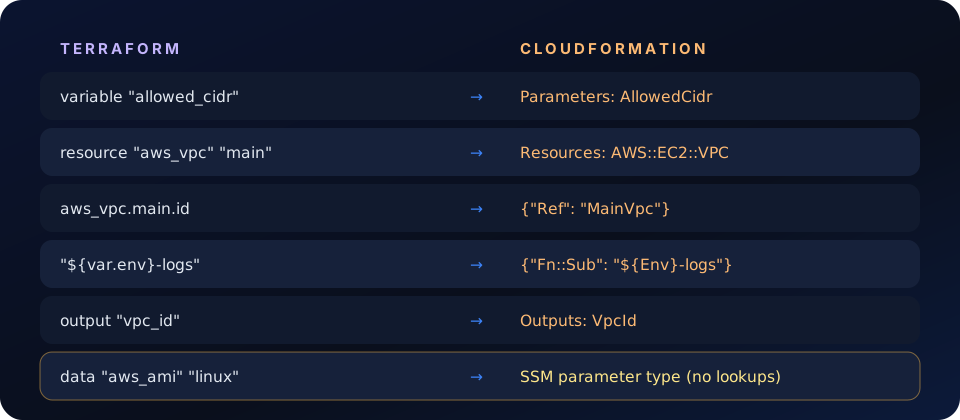
Most of the mapping is direct. Each resource "aws_vpc" becomes an AWS::EC2::VPC entry under Resources, variable blocks become Parameters, and output blocks become Outputs. References such as aws_vpc.main.id turn into intrinsic functions like {"Ref": "MainVpc"} or Fn::GetAtt, and string interpolation becomes Fn::Sub.
Some Terraform features have no plain CloudFormation equivalent. count and for_each usually become repeated resources, unless you opt in to the AWS::LanguageExtensions transform and its Fn::ForEach. Data sources that look things up, such as data "aws_ami", need a parameter or an SSM parameter type instead.
Before you create a stack from the template, validate it with aws cloudformation validate-template and review a change set so you can see exactly what CloudFormation will create.
The template describes new resources. It doesn't adopt the ones Terraform already manages. To move existing resources, use CloudFormation resource import, then remove them from Terraform state with terraform state rm.
Where each kind of Terraform block ends up in the template.
Terraform vs CloudFormation: quick reference
How common Terraform constructs are written in a CloudFormation template. Use it to check the converted JSON line by line.
Terraform concepts and their CloudFormation equivalents
Concept
Terraform
CloudFormation
Input values
variable "env" {}
Parameters with Type, Default and AllowedValues
Resource
resource "aws_s3_bucket" "logs"
"Logs": { "Type": "AWS::S3::Bucket" }
Reference an ID
aws_s3_bucket.logs.id
{ "Ref": "Logs" }
Reference an attribute
aws_s3_bucket.logs.arn
{ "Fn::GetAtt": ["Logs", "Arn"] }
String interpolation
"${var.env}-logs"
{ "Fn::Sub": "${Env}-logs" }
Tags
A map: tags = { Team = "data" }
A list: [{ "Key": "Team", "Value": "data" }]
Optional resource
count = var.enabled ? 1 : 0
A Conditions entry plus "Condition" on the resource
Loops
count, for_each
Repeated resources, or Fn::ForEach with AWS::LanguageExtensions
Lookups
data "aws_ami"
A parameter of type AWS::SSM::Parameter::Value<AWS::EC2::Image::Id>
Explicit ordering
depends_on
DependsOn
Outputs
output "bucket_arn"
Outputs, with an optional Export
Region and state
provider "aws" and terraform.tfstate
Region chosen at deploy time; the stack tracks its resources
Key features
Resources mapped to AWS:: typesEach Terraform resource becomes its CloudFormation type, such as aws_vpc to AWS::EC2::VPC, with arguments renamed to the template's property names.
Variables and outputs carried overvariable blocks become Parameters with their defaults, and output blocks become Outputs.
References become intrinsic functionsAttribute references and interpolated strings are rewritten as Ref, Fn::GetAtt and Fn::Sub.
Nested blocks reshapedBlocks such as ingress and egress become property lists, and tag maps become Key/Value lists.
A JSON template ready to validateThe output is a JSON template you can pass straight to validate-template. Anything without a CloudFormation equivalent is left out, because JSON has no comments.
Secret check before sendingAWS keys, private keys and common API tokens in your HCL are detected in your browser before any code leaves it.
Streaming, copy and downloadThe template appears as it's written. Copy it, wrap long lines, or download it as template.json.
Free, with no signupConvert right away. A free account raises your limits and lists recent conversions on your dashboard.
Examples: Terraform converted to CloudFormation
Three patterns that need more than renaming. Choose Try this example to load the HCL into the converter. The JSON shown is correct output for each snippet; the converter's logical IDs and formatting may differ.
S3 bucket with versioning and tags
Since version 4 of the AWS provider, bucket settings such as versioning are separate Terraform resources. In CloudFormation they're properties of a single AWS::S3::Bucket, and the tag map becomes a list.
A count of 0 or 1 is really a condition. CloudFormation has no boolean parameter type, so the flag becomes a String parameter with allowed values and a Conditions entry.
A source group reference becomes SourceSecurityGroupId with Fn::GetAtt, and the VPC variable can use the AWS::EC2::VPC::Id type so the console offers a picker. Terraform removes the default allow-all egress rule from a group with no egress blocks; CloudFormation keeps it, so add SecurityGroupEgress if you relied on that.
Paste variables and outputs too. They become the template's Parameters and Outputs, so the stack stays configurable.
Replace provider-level settings. The provider "aws" region isn't part of a template. You choose the region when you create the stack.
Check logical IDs. Terraform names like private_a become CloudFormation logical IDs such as PrivateA. Pick names you're happy to keep, because renaming one later replaces the resource.
Watch for fixed names. A hard-coded name, such as a security group's GroupName, stops CloudFormation from replacing that resource during an update. Leave names out unless you need them.
Prefer YAML to read, JSON to generate. CloudFormation accepts both formats, so convert the JSON to YAML afterwards if your team prefers it.
Common mistakes to avoid
Creating a stack over resources Terraform still manages. Two tools managing the same resource leads to drift and failed updates. Import the resources into CloudFormation, then run terraform state rm.
Assuming security group egress is the same. Terraform strips the default allow-all egress rule when a group has no egress blocks. CloudFormation leaves it in place unless you set SecurityGroupEgress.
Losing provider default_tags. Tags set on the provider aren't in any resource block, so they don't reach the template. Add them per resource, or pass stack-level tags when you create the stack.
Hard-coding the region and account. Replace literal values such as us-east-1a or an account ID with AWS::Region, AWS::AccountId and Fn::GetAZs so the template works anywhere.
Expecting boolean parameters. CloudFormation parameters have no boolean type. Use a String parameter with AllowedValues of "true" and "false", then a condition.
Frequently asked questions
How do I convert Terraform to CloudFormation?
Paste your Terraform HCL into the converter at the top of this page and press Convert to CloudFormation. It writes a JSON template with Parameters, Resources and Outputs. Run aws cloudformation validate-template on the result and review a change set before you create the stack.
Can CloudFormation take over resources created by Terraform?
Yes, with resource import. Create a stack or change set that imports each existing resource by its identifier, as described in the AWS import guide, then run terraform state rm so Terraform stops managing them. The guide to migrate a Terraform stack to CloudFormation without downtime walks through the import step by step.
Does the converter read my Terraform state?
No. It only sees the code you paste. It doesn't read state files or plans and has no access to your AWS account, so the template describes what the code declares, not what currently exists. For the trade-offs, see AWS CDK vs Terraform for existing AWS stacks.
What happens to Terraform count and for_each?
CloudFormation has no loops by default, so the converter usually writes each instance as its own resource. A count that switches a resource on or off maps to a condition. For large loops, consider the AWS::LanguageExtensions transform, which adds Fn::ForEach.
Can it convert Terraform modules?
It converts the resources you paste. A module block that points at a registry or Git source can't be expanded, because the converter only sees your code. Paste the module's own resources instead, or model it as a nested stack with AWS::CloudFormation::Stack.
Why is the output JSON rather than YAML?
This tool produces JSON templates, which CloudFormation accepts just like YAML. If you prefer YAML, convert the JSON with a tool such as AWS Labs' cfn-flip.
How do I check the template before deploying?
Run aws cloudformation validate-template --template-body file://template.json for syntax errors, then create a change set to preview every resource CloudFormation will add or change.
Is my code stored?
No. Your code is sent to an AI model hosted on NVIDIA's API only to produce the conversion, and ChatWithCloud doesn't store or log it. Your latest draft is kept only in your browser. For the full picture, see whether it's safe to paste AWS code into an AI converter.
Is the converter free?
Yes. Without an account you can run 6 conversions a minute and 60 a day. A free account raises that to 12 a minute and 200 a day and lists your recent conversions on your dashboard. The guide to ChatWithCloud free converter limits shows how far they stretch for a real migration.